HTTP Headers Checker: All Response Headers & Security Grade
Pricing
from $0.32 / 1,000 checked urls
HTTP Headers Checker: All Response Headers & Security Grade
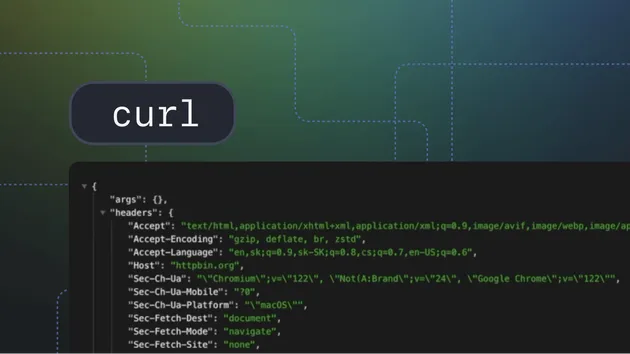
Fetches each URL, one or in bulk, and captures every HTTP response header after redirects. Returns the headers with status, timing, a server fingerprint and an A-F grade for six security headers. For security engineers, DevOps teams, SEO specialists and pentesters.
Pricing
from $0.32 / 1,000 checked urls
Rating
0.0
(0)
Developer
Broke to Built
Maintained by CommunityActor stats
0
Bookmarked
2
Total users
2
Monthly active users
6 days ago
Last modified
Categories
Security
Limited permissionsShare
HTTP Headers Inspector - full headers + security grade + server fingerprint
Send URLs, get every HTTP response header for each, the redirect result, the response time, and a grade of its security headers (HSTS, CSP and more).
| You give it | You get back | You pay (Free plan) |
|---|---|---|
| One URL or a list of up to 25; GET or HEAD | Per URL: status, final URL, timing, all headers, security-header analysis, server fingerprint | $0.0004 per URL |
Pay per result only: no subscription, no start fee. An unreachable URL returns {ok:false, error} and is not charged. Paid Apify plans get Store discounts on the price above.
Example: try it in one click
The input form is already filled in with this example. Press Start and you get the output below.
Real output from that exact input (run on 2026-10-31; long arrays shortened to a few entries and long text cut for display):
Fetch every HTTP response header of any URL, then get a security-header analysis (HSTS, CSP, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy) with an A-F grade and a server fingerprint. Single URL or bulk. Built for security reviews, SEO/tech audits, uptime checks, and agent tool-calls.
$0.0004 per URL checked - cheaper than every paid headers/security-header actor measured on the Store. Failed fetches are recorded free.
What you get
- Every response header captured into a clean JSON object.
- Security grade (A-F) from which hardening headers are present vs missing.
- Server fingerprint -
Server,X-Powered-By,Via. - Status, redirect detection, response timing (ms).
- Single or bulk - one
urlor manyurls, capped bymaxUrls(1-50). - Fail-soft: an unreachable URL returns
{ok:false, error}and is never charged.
Input
Output (real run, 2026-08-07)
An unreachable host comes back uncharged: { "url": "https://bad.invalid", "ok": false, "error": "fetch failed" }
Pricing - $0.0004 per URL, no start fee
Charged once per URL successfully inspected; failed fetches are free. Prices below checked via the Apify Store API on 2026-08-07:
| Actor | Pricing | Per URL |
|---|---|---|
| This actor | $0.0004 per URL | $0.0004 |
| bgfc97/http-security-headers-audit | $0.0005 per url-audited | $0.0005 |
| andok/security-headers-analyzer | $0.001 per dataset item | $0.001 |
| pink_comic/security-headers-checker | $0.0001 start + $0.002 per item | $0.002 |
Limits (honest ones)
- Follows redirects and reports the final response; per-hop headers are not itemized (see our HTTP Status Checker for chains).
maxUrlscapped at 50 per run.- Sites that block non-browser user agents at the CDN may return their block-page headers.
- The security grade reflects header presence, not policy strength (a weak CSP still counts as present).
FAQ
- Does it show every header or just security ones? Every response header, plus a separate security section.
- Can I check many URLs at once? Yes - pass
urls(up to 50). Each successful URL is one charge. - What happens on a dead URL? You get an
{ok:false, error}record and are not charged for it. - Can I use HEAD instead of GET? Yes - set
methodtoHEAD,OPTIONS, etc. - Is the grade an official standard? No - it is a simple present/missing score across six common hardening headers, meant for quick triage.
When not to use this
- You need a security posture score you can hand an auditor. The grade counts how many of six hardening headers are present. It says nothing about whether your CSP is any good. Use a dedicated CSP evaluator for policy strength.
- You need the full redirect chain. Redirects are followed and only the final response is reported. For per-hop status codes and headers, use an HTTP status/redirect chain checker.
- You need TLS certificate details. Cipher suites, chain, expiry and CT logs are not covered - this reads HTTP response headers only.
- You need what a browser sees after JavaScript. Headers come from a plain HTTP request; there is no headless browser, so headers set by service workers or meta-equivalent CSP tags are not included.
- The target blocks non-browser clients. A CDN that challenges the request returns its own block page headers, which will look like a badly configured site rather than an error.
Use from code or AI agents
Callable as an agent tool through the Apify MCP server (mcp.apify.com) - add the actor and your
LLM can inspect headers on demand. Every record with ok:false is a diagnostic, not a result.
Who uses it
- Security engineers grading HSTS, CSP and X-Frame-Options across a list of sites
- DevOps teams confirming cache and security headers after a CDN change
- SEO specialists checking status codes and redirect headers on key URLs
- Pentesters fingerprinting server software from response headers
- Agencies adding a security-header grade to client audits
Changelog
- 2026-11-01: Page text only: the prefilled example now uses a real site instead of a placeholder, the "Try it" output re-run with the new example and the "Try it" block is now headed Example. Code, output and price are unchanged.
- 2026-09-24: New summary at the top of this page: what you send, what you get, the price, and a real output from the prefilled example.