

Subdomain Finder — Certificate Transparency Subdomain Scanner
Pricing
Pay per event
Subdomain Finder — Certificate Transparency Subdomain Scanner
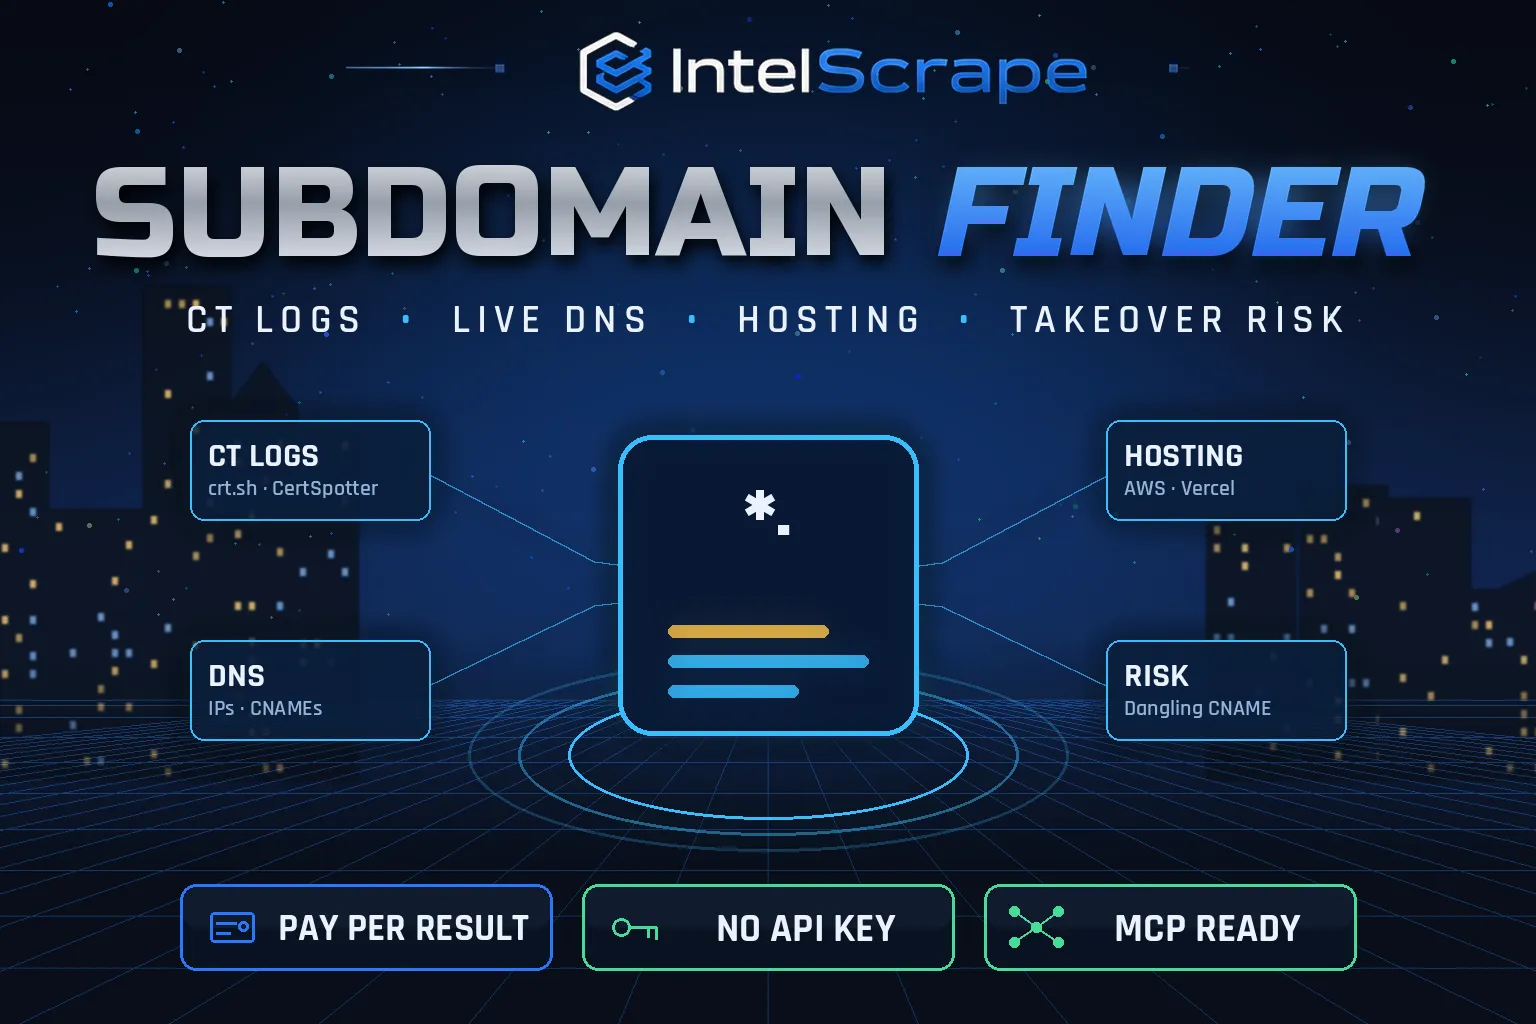
Subdomain Finder: discover every subdomain of a domain from public certificate transparency logs (crt.sh, Cert Spotter), with first/last seen dates, issuers, live DNS (IPs, CNAMEs, hosting provider) and dangling-CNAME and dev/staging flags. Bulk domains. No API key. Pay per subdomain.
Pricing
Pay per event
Rating
0.0
(0)
Developer
IntelScrape
Maintained by CommunityActor stats
0
Bookmarked
2
Total users
1
Monthly active users
6 hours ago
Last modified
Categories
Share
🇨🇳 子域名查找器:从公开的证书透明度日志(crt.sh、Cert Spotter)中发现一个域名的所有子域名,包括首次/最近出现时间、签发机构,以及实时 DNS(IP、CNAME、托管服务商)、悬空 CNAME 风险和开发/测试环境标记。支持批量域名,无需 API 密钥,按子域名付费。
🇸🇬 Pencari Subdomain: temui setiap subdomain sesuatu domain daripada log ketelusan sijil awam (crt.sh, Cert Spotter), dengan tarikh, penerbit, DNS langsung, penyedia hosting dan bendera risiko. Tiada kunci API.
🤖 NEW: Connect This To Your AI!
Use this actor from Claude, ChatGPT, Cursor or any MCP client through the IntelScrape MCP Server, or call it directly over the Apify API.
🏆 Featured Bots by IntelScrape
- Skip Trace Pro
- TruePeopleSearch Scraper
- TikTok Email Scraper
- Amazon Product Reviews Scraper
- Website Contact Scraper
- Skip Trace MCP Server
⚡ Works with n8n, Make, Zapier, Google Sheets and the Apify API.
Passive subdomain discovery from certificate transparency logs with live DNS, hosting provider and takeover-risk flags.
Honest coverage & billing: Passive only: hosts without public certificates are invisible. You pay only for results actually delivered, and a built-in cost guard stops the run at your max-charge limit.
🌍 Built for teams in the US, China and Singapore, and anyone who needs this data in a spreadsheet or pipeline.
⭐ Found it useful? Please leave a review; it helps others find it.
⚖️ Lawful business use only. Collect public data only, and comply with the source site's terms, copyright and data-protection laws (GDPR, CCPA, China PIPL, Singapore PDPA).
Examples below are illustrative; names and values may be fictional or out of date.
What is Subdomain Finder?
Every HTTPS certificate issued today is written to public certificate transparency logs, and each certificate lists the hostnames it covers. That makes CT logs the most complete passive source of subdomains there is: staging servers, admin panels, regional sites, SaaS integrations and forgotten marketing pages all show up. Subdomain Finder searches those logs, de-duplicates every hostname, and checks each one live in DNS so you know what is still running, where it is hosted and which CNAMEs are dangling.
What does it do?
- Certificate transparency search on crt.sh with automatic fallback to Cert Spotter
- De-duplicated hostnames with certificate count, first and last seen dates, latest expiry, issuers and wildcard flag
- Live DNS (on by default): resolves?, A records, CNAME chain
- Hosting provider from CNAMEs: AWS, CloudFront, Azure, Google Cloud, Vercel, Netlify, Heroku, GitHub Pages, Shopify, Zendesk, HubSpot and more
- Dangling CNAME flag: CNAME points to a target that no longer exists (classic subdomain-takeover pattern)
- Dev/admin flag for staging, test, admin, VPN, Jenkins, Grafana-style names
- Bulk: up to 1,000 root domains per run
Why choose us over cheaper scrapers?
- Honest output: limits are documented, missing data is labeled, never invented
- Clean, consistent schema ready for Excel, Sheets, BI tools or an LLM
- No account risk: no logins, no cookies, no API keys
- Pay per result with a built-in cost guard; no subscription, failed items are never charged
- Fast and light: no residential proxy, so runs finish in seconds and stay cheap
- Maintained by IntelScrape and fixed fast when the source changes
Who is it for?
- Attack-surface mapping for security teams and bug bounty hunters (passive, no scanning)
- Subdomain takeover checks on your own estate
- Competitive intelligence: see which SaaS tools and regions a company runs
- Lead generation: find companies using Zendesk, HubSpot or Shopify by subdomain
- Asset inventory and M&A due diligence
- SEO: find forgotten subdomains that leak duplicate content
How to use it
In Apify Console (no code)
- Click Try for free / Start. The form is prefilled with a working example.
- Change the inputs (see examples below).
- Click Start, then export the results as JSON, CSV, Excel, XML or HTML, or open them in Google Sheets.
- Optional: Schedule the actor to run hourly, daily or weekly.
Via API
Or use the official Apify JavaScript and Python clients:
With AI agents (MCP)
Add Apify's MCP server (https://mcp.apify.com) or the IntelScrape MCP Server to Claude Desktop, Cursor, ChatGPT or any MCP client, then ask in plain language, e.g. "Run intelscrape/subdomain-finder with the default input and summarise the results."
Input examples
One domain, 100 most recent with DNS (default)
Many domains, certificate data only
Output fields
| Field | Description |
|---|---|
domain / subdomain / level | Root domain, hostname and depth |
certCount / firstSeen / lastSeen / certValidUntil / hasValidCert | Certificate history |
issuers / wildcardCert | Certificate authorities and wildcard coverage |
resolves / ips / cnames | Live DNS (when resolveDns is on) |
hostingProvider | Detected from CNAMEs |
danglingCnameRisk | CNAME exists but target does not resolve (NXDOMAIN) |
looksSensitive | Name suggests dev, staging, admin or internal tooling |
source | crt.sh or certspotter |
Sample output
Pricing (pay per event)
| Event | When it is charged | Price |
|---|---|---|
| Actor start | once per run | $0.005 |
| Subdomain | per unique subdomain row | $0.001 |
| DNS resolve | per subdomain checked live (on by default; turn off to skip) | $0.0005 |
Cost examples
| Run | Cost |
|---|---|
| Default run (apify.com: 36 subdomains with DNS) | $0.059 |
| 50 domains × 200 subdomains, no DNS | $10.005 |
| Monthly check of 1 domain, 1,000 subdomains with DNS | $1.505 |
Platform usage is included in these prices. Set Max charge per run in the run options to cap spend; the actor stops cleanly when the limit is reached and keeps everything collected so far.
Tips for best results
- Set includeExpired to false for a current-only view.
- Filter danglingCnameRisk = true on your own domains and fix those records first.
- Turn off DNS to get the cheapest raw inventory.
- Very large domains (google.com) have millions of certificates; crt.sh may time out and the actor falls back to Cert Spotter, which returns a smaller recent window.
FAQ
Is this active scanning?
No. It only reads public certificate logs and public DNS resolvers; nothing touches the target servers.
Will it find every subdomain?
It finds every hostname that has ever appeared on a publicly logged certificate. Hosts that never had a public certificate (internal-only, HTTP-only) cannot be found passively.
Why does a subdomain not resolve?
It may be retired, internal or behind split DNS. The certificate history still shows it existed.
What is dangling CNAME risk?
The subdomain points (CNAME) to a target that returns NXDOMAIN, the usual pre-condition for subdomain takeover. Verify manually; this is a flag, not proof.
Do I need an API key?
No.
Is failure charged?
No. If both certificate sources are down the domain is logged and not charged.
Honest limits
- Passive only: hosts without public certificates are invisible.
- crt.sh is a free community service and can be slow or time out on huge domains.
- Wildcard certificates hide the individual hostnames they cover.
- Hosting detection uses CNAMEs; hosts on bare A records show no provider.
Related IntelScrape bots
- Tech Stack Detector: CMS, analytics & frameworks per domain
- SPF DMARC Checker: email security records per domain
- WHOIS Domain Lookup: registrar, dates & owner data
- WordPress Theme & Plugin Detector: themes, plugins & versions
- Open Graph Scraper: link previews & meta tags
- Skip Trace MCP Server: IntelScrape tools for AI agents
Legal
This actor collects publicly available data only. You are responsible for using the results lawfully and in line with the source's terms and applicable privacy laws (GDPR, CCPA, PIPL, PDPA). Process personal data only with a legitimate purpose. IntelScrape is not affiliated with, endorsed by or sponsored by the data source; all trademarks belong to their owners.


