
CMS & Hosting Detector — Website Tech Stack, Bulk, Keyless
Pricing
from $67.00 / 1,000 tech detections
CMS & Hosting Detector — Website Tech Stack, Bulk, Keyless
CMS and hosting detector: per URL, the CMS, frameworks, analytics, payments and web server (56 common technologies) plus the hosting/CDN provider, with confidence scores. Keyless; not a full Wappalyzer or BuiltWith replacement. Part of NexGen Signal — data tools and official-source data products
Pricing
from $67.00 / 1,000 tech detections
Rating
0.0
(0)
Developer
NexGen Signal
Maintained by CommunityActor stats
0
Bookmarked
1
Total users
0
Monthly active users
3 days ago
Last modified
Categories
Share
Answer two questions per website: what is it built with, and where is it hosted? Give one URL or a long list and get, per site, the CMS or site builder, JavaScript framework, analytics, payments, ecommerce platform and web server it runs — plus the hosting/CDN provider (Cloudflare, CloudFront, Fastly, Vercel, Netlify and more) as its own field, and a 0–100 confidence score on every detection.
Pay per site. No API key, no headless browser, no personal data. It reads the public HTTP response — headers, cookies, scripts and meta tags — and matches 56 widely used technologies across 17 categories. Wappalyzer and BuiltWith recognise thousands; this is the fast, keyless check of the common stack you can call from code, an AI agent or an automation flow.
Typical jobs: "which of these 2,000 prospects run Shopify?", "what CMS is this competitor on?", "which of our vendors sit behind Cloudflare?".
What this is, in one paragraph
Every website announces a surprising amount about how it is built, right in its public HTTP response: the Server header, the cookies it sets, the scripts and meta tags in its HTML, the CDN fingerprints in its headers. This actor fetches each site's public homepage (following redirects, with retry-in-front hardening), reads those signals, and matches them against a signature library spanning content-management systems, website builders, ecommerce platforms, JavaScript frameworks and libraries, analytics and tag managers, live-chat and marketing tools, payment SDKs, CDNs, hosting providers, web servers, and back-end languages. Each match carries a confidence score, and — the upgrade over a plain Wappalyzer clone — the hosting/CDN provider is surfaced as its own field so you can see not just what a site runs but where it runs. No login, no headless browser, no personal data.
Who buys this and for what job
- Sales and go-to-market teams qualifying prospects by the tech they run — "show me every prospect on Shopify" or "who is still on WordPress".
- Competitive-intelligence analysts profiling a market's technology choices across hundreds of domains at once.
- Security and due-diligence teams taking a first-pass inventory of a target's public stack and hosting footprint.
- Developers who want a keyless check of a site's common stack they can call directly from code or an agent.
Buyers usually search for this as "CMS detector", "what is this website built with" or "tech stack detector".
The upgrade over a plain detector
Two things set this apart from a plain detector. First, hosting/CDN detection: the record carries a dedicated hosting_cdn field that names the edge/hosting provider (Cloudflare, CloudFront, Fastly, Akamai, Vercel, Netlify, GitHub Pages, Amazon S3, and more) inferred from response headers — the layer a category-only detector blurs into "CDN". Second, a per-technology confidence score (0–100) on every detection, so you can keep only high-confidence matches when accuracy matters and treat weaker HTML-pattern hits with appropriate caution.
Sample output
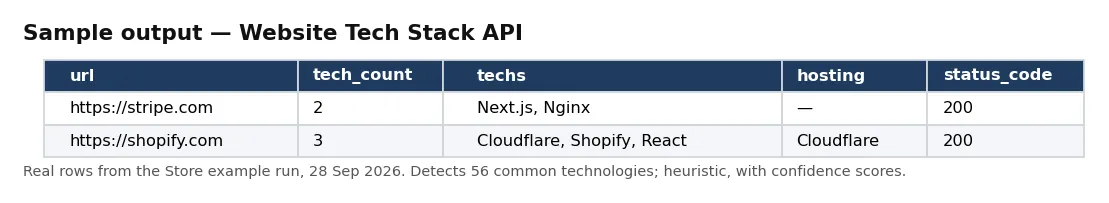
Real rows from a live run of this actor (first 5 rows, selected columns).
One full record from the same run, exactly as delivered:
Pricing
| Event | Free plan | Bronze | Silver | Gold / Platinum / Diamond |
|---|---|---|---|---|
tech-detection | $0.10 | $0.09 | $0.08 | $0.067 |
One tech-detection per site delivered. Delivered before charged — a site that fails to fetch still returns a record (with the error captured) and is billed as a delivered detection, exactly as a Wappalyzer-style API would count a scanned URL.
Input
| Field | Type | Default | Description |
|---|---|---|---|
urls | array/string | — | One or more site URLs or domains to scan. |
domains / websites / targetUrls | array | — | Aliases for urls (bare domains are accepted and normalised to https). |
url | string | — | A single site URL or domain. |
categories_filter | array | [] | Keep only technologies in these categories (e.g. CDN, CMS, Analytics). Empty = all. |
include_confidence | boolean | true | Add a per-technology confidence score (0–100). |
include_versions | boolean | true | Add a per-technology version where detectable. |
timeout_seconds | integer | 15 | Per-site fetch timeout (1–60). |
Provide URLs through whichever field your workflow prefers — urls, domains, websites, targetUrls, or a single url. Bare domains like example.com are normalised to https://example.com, and duplicates are removed.
Output
One JSON object per site. Real example (values as detected):
An unbilled RUN_RECEIPT records how many sites were delivered and whether charged equals delivered.
Field reference
Each record carries: record_id and url (the input URL), final_url (after redirects), status_code, tech_count, categories (the distinct category list), technologies (the detailed list — each with name, category, optional version, and optional confidence), tech_names (the flat name list for quick filtering), hosting_cdn (the inferred hosting/CDN providers), scan_time_ms, and error (null on success, or the fetch error). Provenance travels on every record: source, source_url, licence, attribution, disclaimer, and observed_at.
How a run works
For each URL, the actor issues a single GET with a real browser User-Agent, following redirects, with retry-in-front hardening — up to four attempts with a short backoff before a site is recorded as failed. It reads the response's status, final URL, headers, cookies, and HTML, then runs the signature library over those signals. Header and cookie signatures (a CF-RAY header, a _shopify cookie, Server: nginx) score highest; HTML-pattern signatures (a __NEXT_DATA__ blob, a js.stripe.com script) score a notch lower. The detected technologies are de-duplicated to the highest-confidence hit per technology, categories and hosting/CDN are rolled up, and one record is delivered and charged.
Working with the data
Because every technology carries a confidence, a pipeline can keep only detections at or above a threshold — high-confidence header and cookie hits — when precision matters, and fall back to the full list when recall matters. The hosting_cdn field lets you segment a domain list by where it is hosted, not just what it runs, which is often the more actionable cut for infrastructure and security work. The tech_names array is the quick filter — "give me every domain where tech_names contains Shopify" — while the technologies array carries the structured detail for reporting. Feed a list of ten thousand domains and get a complete technographic table back in one run.
Honest limitations
- Heuristic, not certified. Detections are inferred from public HTTP signals and carry a confidence score; they are best-effort, not a guarantee. Treat low-confidence HTML-pattern hits accordingly.
- Homepage-scoped. The scan reads each site's public homepage response; technologies only loaded on inner pages or behind a login are not seen.
- No bot-detection circumvention. The actor makes an honest browser-headed request and retries transient failures; it does not attempt to defeat anti-bot systems, so a hard-blocked site returns a record with the error captured.
- No person data. Only public technical signals are read; no login is performed and no personal data is emitted.
Use with AI agents
Point Claude, an OpenAI Agents SDK tool, an n8n or Make flow, or any MCP-aware client at this actor and hand it a list of domains. Because the output is clean, flat JSON with a tech_names array and a hosting_cdn field, an agent can filter and reason over the result without any post-processing — "which of these prospects run Shopify and sit behind Cloudflare?" is answerable directly from one run's dataset. A typical agent prompt is simply: run the tech-stack detector on my list of domains and return the structured results, keeping only detections with confidence 90 or above.
Differentiation
A lightweight, keyless tech-stack check for the 56 most common technologies (Wappalyzer and BuiltWith cover far more), with a dedicated hosting/CDN field and a per-technology confidence score. Keyless, pay-per-site, callable from code or an AI agent, and priced per site with a Gold-tier discount ladder for volume.
Technology detection derived from each site's own publicly served HTTP response (headers, cookies, HTML). Public technical signals only; no login, no personal data. Detection is heuristic and provided as-is.


