
Company Career Page Scraper — Greenhouse, Lever & Ashby Jobs
Pricing
from $80.00 / 1,000 jobs
Company Career Page Scraper — Greenhouse, Lever & Ashby Jobs
Company career page scraper: pull careers page jobs from company Greenhouse, Lever and Ashby boards via their official public APIs — title, location, department, apply URL. No login, no blocking.
Pricing
from $80.00 / 1,000 jobs
Rating
0.0
(0)
Developer
NexGenData
Maintained by CommunityActor stats
0
Bookmarked
5
Total users
0
Monthly active users
9 days ago
Last modified
Categories
Share
Same product as ATS Job Aggregator (nexgendata/ats-job-aggregator) — this actor now runs the same code (Greenhouse, Lever, Ashby, SmartRecruiters, Workday) and returns the same fields. Priced per Job row.
Company Career Page Scraper — Greenhouse, Lever & Ashby Jobs
A company career page scraper: give it company names or board slugs and get their careers page jobs from Greenhouse, Lever and Ashby.
Every major ATS in one schema — aggregate job postings across Greenhouse, Lever, Workday, Workable and more for full hiring-market coverage.
📊 Sample Output
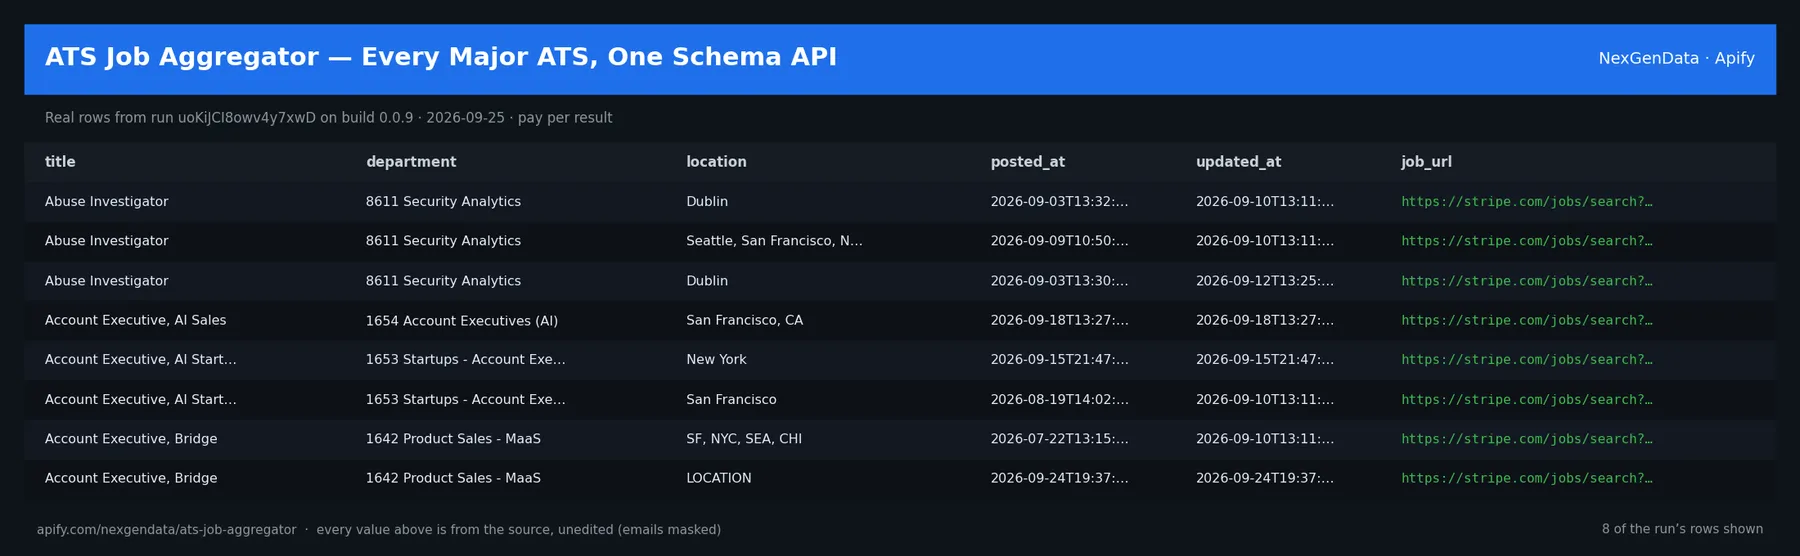
company | title | department | location | posted_at | updated_at |
|---|---|---|---|---|---|
| stripe | Abuse Investigator | 8611 Security Analytics | Dublin | 2026-09-03T13:32:53-04:00 | 2026-09-10T13:11:58-04:00 |
| stripe | Abuse Investigator | 8611 Security Analytics | Seattle, San Francisco, New York City | 2026-09-09T10:50:29-04:00 | 2026-09-10T13:11:58-04:00 |
| stripe | Abuse Investigator | 8611 Security Analytics | Dublin | 2026-09-03T13:30:34-04:00 | 2026-09-12T13:25:25-04:00 |
| stripe | Account Executive, AI Sales | 1654 Account Executives (AI) | San Francisco, CA | 2026-09-18T13:27:51-04:00 | 2026-09-18T13:27:51-04:00 |
| stripe | Account Executive, AI Startups - Grower | 1653 Startups - Account Executives (NA) | New York | 2026-09-15T21:47:18-04:00 | 2026-09-15T21:47:18-04:00 |
| stripe | Account Executive, AI Startups (Hunter) | 1653 Startups - Account Executives (NA) | San Francisco | 2026-08-19T14:02:07-04:00 | 2026-09-10T13:11:58-04:00 |
Real rows from run uoKiJCI8owv4y7xwD on build 0.0.9 (2026-09-25), unedited apart from masked emails/phones and shortened long text; fields the source does not publish are empty.
⚙️ Sample inputs
This is the Store example input — the same input Apify's automated check runs — so it is proven to return rows on the current build. Paste it into the input form, or send it through the API, CLI or a schedule:
🔧 Input reference
| Field | Type | Default | What it does |
|---|---|---|---|
companies (required) | array | ["greenhouse:stripe", "ashby:ramp", "lever:spotify"] | Career boards to scrape, pulled DIRECTLY from each employer's ATS. Each entry can be: (1) a board URL (we auto-detect the ATS + company) such as https://boards.greenhouse.io/strip… |
keywords | array | [] | Optional. Only return jobs whose title contains one of these (case-insensitive) words/phrases, e.g. ['engineer', 'data', 'remote']. Leave empty to return all open roles. |
maxJobs | integer | 100 | Hard cap on the total number of jobs returned across all boards in this run. 0 = no cap (return all matching open jobs). |
enrichWorkday | boolean | true | Workday only. When on, each Workday job is enriched with a per-job detail request to fill description, employment type, posted date and req id (slower, more requests). When off, o… |
notionConnector | string | Optional. Connect your Notion workspace and the run also writes the jobs as a Notion page - the Actor never sees your Notion credentials. Authorize a Notion MCP connector in Apify… | |
notionParentId | string | Optional. The Notion page ID to create the page under. If blank, Notion creates a private page in your workspace. | |
supabaseConnector | string | Optional. Connect your own Supabase project and the results are also inserted into a table in the same run — the Actor never sees your Supabase credentials. Authorize a write-scop… | |
supabaseTable | string | "nexgendata_leads" | Target table in the public schema (created if missing, with id, a jsonb data column, and a scraped_at timestamp). Default: nexgendata_leads. |
supabaseProjectId | string | Your Supabase project reference (e.g. abcdefghijklmnop). Required unless your connector URL is already project-scoped. Find it in your project URL: supabase.com/dashboard/project/… | |
deliveryDedup | boolean | true | When on (default), records already delivered in a previous run are not delivered again to the same destination — so scheduled runs only push new items. Turn off to deliver every r… |
🧾 JSON sample record
One real record from run uoKiJCI8owv4y7xwD (emails/phones masked, long text shortened):
💰 Pricing
| Event | Price (USD) | When it is charged |
|---|---|---|
Actor Start (apify-actor-start) | $0.005 | Charged when the Actor starts running. Number of events charged depends on Actor memory (one event per GB, minimum one event). |
Job (job-record) | $0.08 | Charged per job posting extracted and normalized from any supported ATS (Greenhouse, Lever, Ashby, SmartRecruiters, Workday) into your dataset. |
Pay-per-event: you pay only for what the run delivers. A run that delivers nothing bills no result events (only the actor-start event, when the actor defines one). Example: a run that delivers 100 results costs 100 × $0.08 = $8.00 plus the start fee.
🔗 Related Actors
More from the NexGenData Jobs & hiring signals family:
- Company Job Board Scraper — Careers Page Jobs API
- Foundit India Jobs Scraper — Salaries & Skills, No API Key
- Greenhouse Jobs Scraper — Hiring Data API
4 more in this family on the NexGenData Store page.
⏰ Run this as a weekly hiring monitor (recommended)
Point it at a watchlist of companies and schedule a weekly sweep (0 8 * * 1). New roles become an always-on hiring-signal feed — see who's scaling which teams, week over week, before it's obvious.
📊 What you get
Clean JSON, one record per job record (full output has 15 fields):
company— Companytitle— Titledepartment— Departmentteam— Teamlocation— Locationremote— Remoteemployment_type— Employment typeposted_at— Posted atupdated_at— Updated atjob_url— Job url
Pricing: $0.08 per job record (Pay-Per-Event) — about 12 job records per $1.
🤖 Use with AI agents
Point Claude, the OpenAI Agents SDK, an n8n flow or any MCP-aware client at it and pull hiring data on demand.
Agentic payments (x402): Supports agentic payment via x402 — agents can call this actor with USDC, no API key required.
🔗 Related jobs & hiring actors
The ATS family — every major ATS, one schema: Greenhouse · Lever · Workday · Workable & SmartRecruiters · Company Job Board
Other job sources: HN Who's Hiring · We Work Remotely · H-1B Salary Search
Hiring-intelligence layer (signals): Hiring Signal Detector · Hiring Signals to Notion · Tech Hiring Signals
Deepest single source — LinkedIn Jobs Scraper: LinkedIn Jobs Scraper
APAC coverage: Singapore MyCareersFuture
Agent front door — Job Market MCP: Job Market MCP
Public job-posting and hiring-signal data.


