
CVE Vulnerability Monitor — NVD, CISA KEV & EPSS
Pricing
from $30.00 / 1,000 cves
CVE Vulnerability Monitor — NVD, CISA KEV & EPSS
Monitor new/updated CVEs by vendor or product, enriched with CISA KEV exploited-flag and EPSS exploit probability. Official NVD data, no login.
Pricing
from $30.00 / 1,000 cves
Rating
0.0
(0)
Developer
NexGenData
Maintained by CommunityActor stats
0
Bookmarked
3
Total users
2
Monthly active users
17 days ago
Last modified
Categories
Share
CVE Vulnerability Monitor
NVD, CISA KEV & EPSS
📊 Sample Output
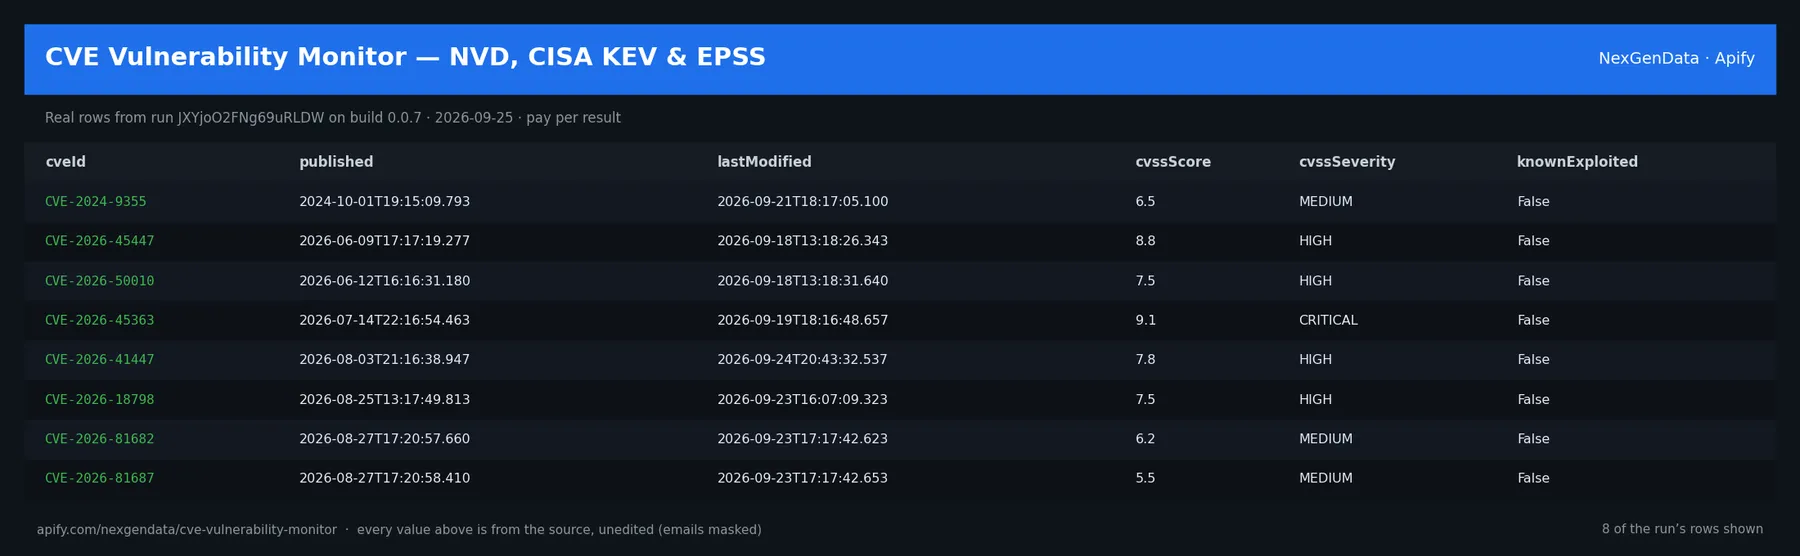
cveId | published | lastModified | cvssScore | keyword | epssScore |
|---|---|---|---|---|---|
| CVE-2024-9355 | 2024-10-01T19:15:09.793 | 2026-09-21T18:17:05.100 | 6.5 | openssl | 0.00298 |
| CVE-2026-45447 | 2026-06-09T17:17:19.277 | 2026-09-18T13:18:26.343 | 8.8 | openssl | 0.02167 |
| CVE-2026-50010 | 2026-06-12T16:16:31.180 | 2026-09-18T13:18:31.640 | 7.5 | openssl | 0.00721 |
| CVE-2026-45363 | 2026-07-14T22:16:54.463 | 2026-09-19T18:16:48.657 | 9.1 | openssl | 0.00364 |
| CVE-2026-41447 | 2026-08-03T21:16:38.947 | 2026-09-24T20:43:32.537 | 7.8 | openssl | 0.00168 |
| CVE-2026-18798 | 2026-08-25T13:17:49.813 | 2026-09-23T16:07:09.323 | 7.5 | openssl | 0.01537 |
Real rows from run JXYjoO2FNg69uRLDW on build 0.0.7 (2026-09-25), unedited apart from masked emails/phones and shortened long text; fields the source does not publish are empty.
⚙️ Sample inputs
This is the Store example input — the same input Apify's automated check runs — so it is proven to return rows on the current build. Paste it into the input form, or send it through the API, CLI or a schedule:
🔧 Input reference
| Field | Type | Default | What it does |
|---|---|---|---|
keywords (required) | array | ["openssl", "fortinet"] | Terms to monitor, e.g. ["openssl","fortinet","apache log4j"]. |
sinceDays | integer | 7 | Return CVEs modified within this many days. |
maxPerKeyword | integer | 20 | Cap CVEs returned per keyword. |
severityMin | string | "" | Optional floor: LOW, MEDIUM, HIGH, or CRITICAL. |
🧾 JSON sample record
One real record from run JXYjoO2FNg69uRLDW (emails/phones masked, long text shortened):
💰 Pricing
| Event | Price (USD) | When it is charged |
|---|---|---|
Actor Start (apify-actor-start) | $0.005 | Charged when the Actor starts running. Number of events charged depends on Actor memory (one event per GB, minimum one event). |
Cve (cve-record) | $0.03 | Charged per CVE. |
Pay-per-event: you pay only for what the run delivers. A run that delivers nothing bills no result events (only the actor-start event, when the actor defines one). Example: a run that delivers 100 results costs 100 × $0.03 = $3.00 plus the start fee.
🔗 Related Actors
More from the NexGenData US government, courts & regulators family:
- CourtListener Federal Docket Scraper — RECAP API
- US Federal & State Judges Database API
- US Court Oral Argument Recordings Index API
- EPA ECHO Enforcement Scraper — Violations API
- EPA TRI Toxic Release Facilities — Records API
- FAA Airworthiness Directives + NASA ASRS Safety API
46 more in this family on the NexGenData Store page.
⏰ Schedule it
Run on a schedule (0 8 * * 1) to monitor changes over time — an always-on CVE watch.
📊 What you get
Clean JSON output (10 fields):
cveId— Cve Idpublished— PublishedlastModified— Last ModifiedcvssScore— Cvss ScorecvssSeverity— Cvss SeverityknownExploited— Known Exploitedkeyword— Keyworddescription— Description
Pricing: $0.030 per CVE (Pay-Per-Event) — about 33 CVEs per $1.
🤖 Use with AI agents
Point Claude, the OpenAI Agents SDK, an n8n flow or any MCP-aware client at it.
Sample agent prompt:
Agentic payments (x402): Supports agentic payment via x402 — call this actor with USDC, no API key required.
🔗 Related tools — Security audit toolkit
SSL Checker · DMARC Auditor · Domain Security Posture · CISA KEV · Dependency Advisories · Chrome Extension Analyzer
A NexGenData utility actor.


