

CISA KEV + EPSS Vulnerability Intelligence Tracker
Pricing
from $50.00 / 1,000 enriched cves
CISA KEV + EPSS Vulnerability Intelligence Tracker
Track CISA Known Exploited Vulnerabilities (KEV) with EPSS scores — CVE, vendor, product, date added, due date and required action — as clean JSON for security teams and agents.
Pricing
from $50.00 / 1,000 enriched cves
Rating
0.0
(0)
Developer
NexGenData
Maintained by CommunityActor stats
0
Bookmarked
2
Total users
1
Monthly active users
a day ago
Last modified
Categories
Share
A focused utility for developers and agents.
📊 Sample Output
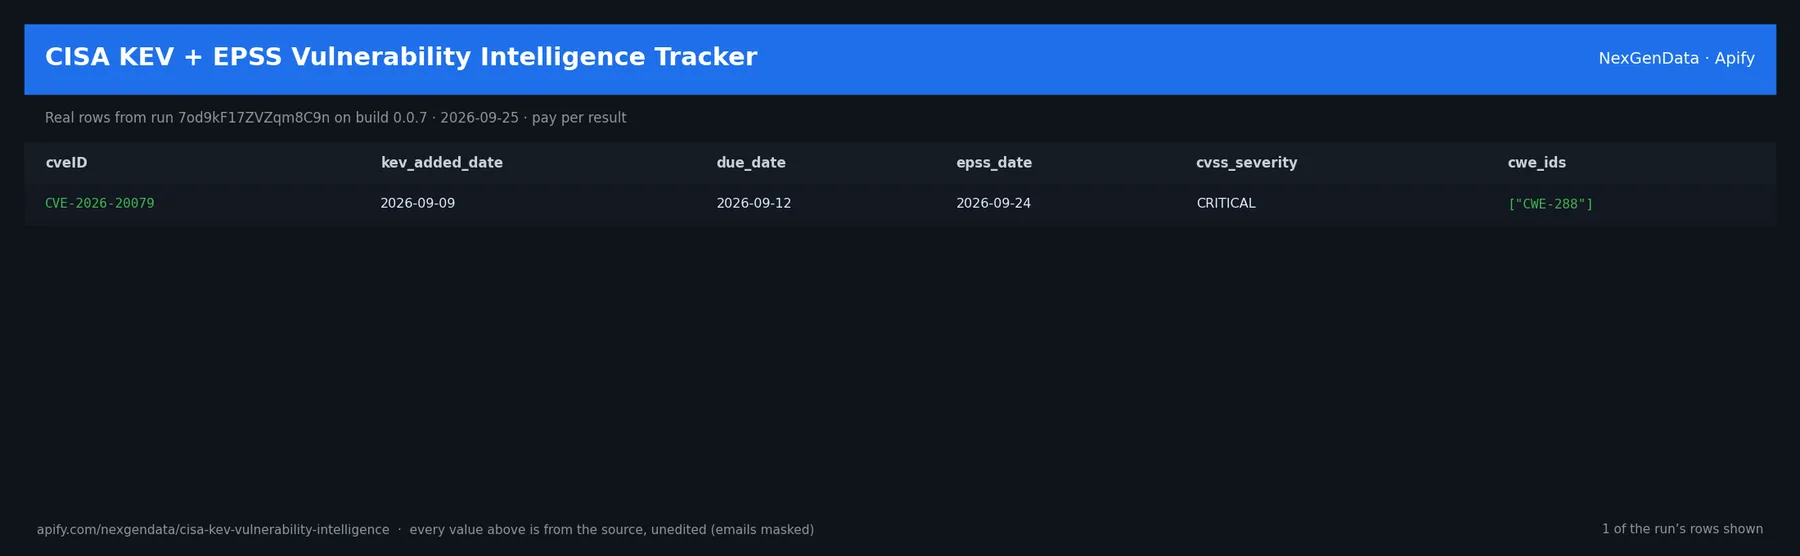
cveID | kev_added_date | due_date | epss_score | epss_percentile | epss_date |
|---|---|---|---|---|---|
| CVE-2026-20079 | 2026-09-09 | 2026-09-12 | 0.8818 | 0.99765 | 2026-09-24 |
Real rows from run 7od9kF17ZVZqm8C9n on build 0.0.7 (2026-09-25), unedited apart from masked emails/phones and shortened long text; fields the source does not publish are empty.
⚙️ Sample inputs
This is the Store example input — the same input Apify's automated check runs — so it is proven to return rows on the current build. Paste it into the input form, or send it through the API, CLI or a schedule:
🔧 Input reference
| Field | Type | Default | What it does |
|---|---|---|---|
vendor_filter | string | "" | Substring match on the CISA KEV vendorProject field (case-insensitive). Examples: 'microsoft', 'cisco', 'fortinet'. Leave empty to include every vendor in the KEV catalog window. |
min_epss_score | string | "0.5" | Filter CVEs whose EPSS exploit-probability score is below this threshold (parsed as a float in [0,1]). EPSS ≥ 0.5 typically flags vulnerabilities with elevated near-term exploitat… |
days_back | integer | 30 | How many days back from today to include CISA KEV catalog additions. Default 30 captures the freshest entries (typical triage window). Max 365. |
max_cves | integer | 100 | Hard cap on the number of CVEs to enrich and push to the dataset (KEV records are sorted newest-first before the cap). Each enriched CVE is a billable record. Range 1-2000. |
🧾 JSON sample record
One real record from run 7od9kF17ZVZqm8C9n (emails/phones masked, long text shortened):
💰 Pricing
| Event | Price (USD) | When it is charged |
|---|---|---|
Actor Start (apify-actor-start) | $0.005 | Charged when the Actor starts running. Number of events charged depends on Actor memory (one event per GB, minimum one event). |
Enriched CVE (cve-enriched) | $0.05 | Per CVE enriched with KEV + EPSS + NVD CVSS + affected products |
Pay-per-event: you pay only for what the run delivers. A run that delivers nothing bills no result events (only the actor-start event, when the actor defines one). Example: a run that delivers 100 results costs 100 × $0.05 = $5.00 plus the start fee.
🔗 Related Actors
More from the NexGenData US government, courts & regulators family:
- CFPB HMDA Mortgage Lending Records API
- CFTC COT Enhanced — Position Velocity & Percentile Tracker
- CFTC Enforcement Actions Tracker — Case Records API
- Colorado Business Entity Search — CO Registry Lookup API
- Connecticut Business Registry Search — CT Entity Data API
- Contractor License Leads — Licensed US Contractor Prospects API
46 more in this family on the NexGenData Store page.
⏰ Schedule it
Run on a schedule (0 8 * * 1) to monitor changes over time — an always-on CVE watch.
📊 What you get
Clean JSON output (20 fields):
cveID— Cve IDvendor— Vendorproduct— Productvulnerability_name— Vulnerability namekev_added_date— Kev added datedue_date— Due daterequired_action— Required actionshort_description— Short description
Pricing: $0.05 per CVE (Pay-Per-Event) — about 20 per $1. Actor start fee $0.005 per run. Live prices are in the Pricing table below.
🤖 Use with AI agents
Point Claude, the OpenAI Agents SDK, an n8n flow or any MCP-aware client at it.
Sample agent prompt:
Agentic payments (x402): Supports agentic payment via x402 — call this actor with USDC, no API key required.
🔗 Related tools — Security audit toolkit
SSL Checker · DMARC Auditor · Domain Security Posture · CVE Monitor · Dependency Advisories · Chrome Extension Analyzer
This actor is currently private — treated and ready for review.
A NexGenData utility actor.


