
SSL Certificate Checker — Bulk Expiry & Chain Monitor
Pricing
from $10.00 / 1,000 certificate checks
SSL Certificate Checker — Bulk Expiry & Chain Monitor
Bulk SSL/TLS certificate checker: for a list of domains, returns validity, expiry/days-remaining, issuer, subject, SANs, protocol, and cipher. For DevOps, security, and cert-expiry monitoring.
Pricing
from $10.00 / 1,000 certificate checks
Rating
0.0
(0)
Developer
NexGenData
Maintained by CommunityActor stats
0
Bookmarked
10
Total users
1
Monthly active users
7 days ago
Last modified
Categories
Features
Share
SSL Certificate Checker
SSL Certificate Checker is a NexGenData tool on Apify that returns certificate validity, expiry, issuer, SANs, protocol and cipher from each domain's live TLS handshake.
Bulk Expiry & Chain Monitor
Expired and invalid certificates are delivered as rows. If a certificate fails verification (expired, self-signed, wrong host, untrusted issuer), the actor still reads it and returns a row with
isValid: falseand thereason(for example "certificate has expired"). These rows are charged like any other row. Domains that cannot be reached at all (timeout, no TLS) are listed in the status message and not charged.
📊 Sample Output
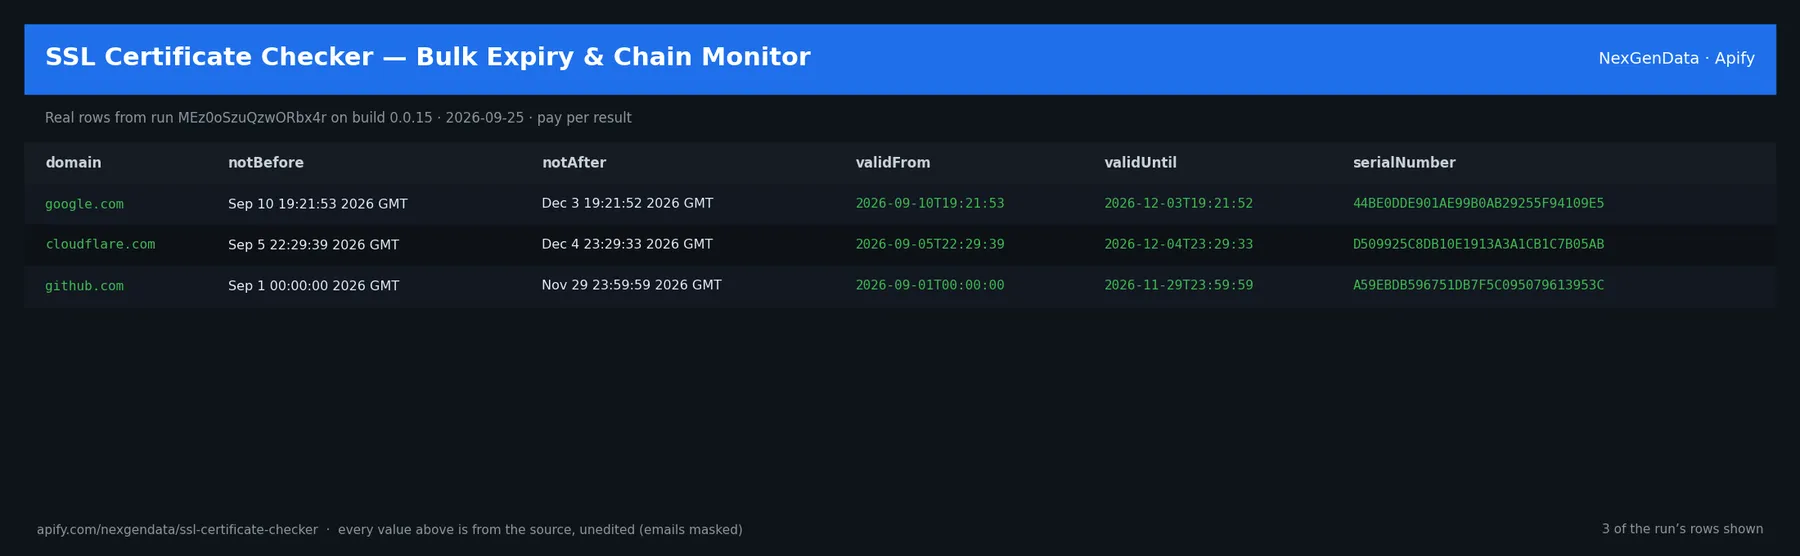
domain | notBefore | notAfter | validFrom | validUntil | serialNumber |
|---|---|---|---|---|---|
| google.com | Sep 10 19:21:53 2026 GMT | Dec 3 19:21:52 2026 GMT | 2026-09-10T19:21:53 | 2026-12-03T19:21:52 | 44BE0DDE901AE99B0AB29255F94109E5 |
| cloudflare.com | Sep 5 22:29:39 2026 GMT | Dec 4 23:29:33 2026 GMT | 2026-09-05T22:29:39 | 2026-12-04T23:29:33 | D509925C8DB10E1913A3A1CB1C7B05AB |
| github.com | Sep 1 00:00:00 2026 GMT | Nov 29 23:59:59 2026 GMT | 2026-09-01T00:00:00 | 2026-11-29T23:59:59 | A59EBDB596751DB7F5C095079613953C |
Real rows from run MEz0oSzuQzwORbx4r on build 0.0.15 (2026-09-25), unedited apart from masked emails/phones and shortened long text; fields the source does not publish are empty.
⚙️ Sample inputs
This is the Store example input — the same input Apify's automated check runs — so it is proven to return rows on the current build. Paste it into the input form, or send it through the API, CLI or a schedule:
🔧 Input reference
| Field | Type | Default | What it does |
|---|---|---|---|
domains | array | ["google.com", "github.com", "cloudflare.com"] | List of domains/hostnames to check SSL certificates for (bulk). One result per domain. |
domain | string | Optional single domain, added to the list. Kept for backward compatibility. | |
port | integer | 443 | TLS port (default 443). |
concurrency | integer | 10 | Domains checked in parallel. |
🧾 JSON sample record
One real record from run MEz0oSzuQzwORbx4r (emails/phones masked, long text shortened):
💰 Pricing
| Event | Price (USD) | When it is charged |
|---|---|---|
Actor Start (apify-actor-start) | $5e-05 | Charged when the Actor starts running. Number of events charged depends on Actor memory (one event per GB, minimum one event). |
Certificate check (apify-default-dataset-item) | $0.01 | Single result in the default dataset. |
Pay-per-event: you pay only for what the run delivers. A run that delivers nothing bills no result events (only the actor-start event, when the actor defines one). Example: a run that delivers 100 results costs 100 × $0.01 = $1.00 plus the start fee.
🔗 Related Actors
More from the NexGenData Leads, contacts & enrichment family:
- Shopify App Merchant Finder — Competitor App User Leads API
- Shopify Store Analyzer — Catalog, Apps & Revenue Signals API
- Shopify Store Detector — Tech, Theme & App Detection API
- TikTok Creator Email Finder — Influencer Contact API
- Tech Stack Detector — Wappalyzer & BuiltWith API Alternative
- Website Email Extractor — Bulk Contact Scraper
30 more in this family on the NexGenData Store page.
⏰ Schedule it
Run on a schedule (0 8 * * 1) to monitor changes over time — an always-on domain watch.
📊 What you get
Clean JSON output (21 fields):
domain— Domainport— PortisValid— Is ValidisExpired— Is Expiredreason— why verification failed (only onisValid: falserows)isExpiringSoon— Is Expiring SoondaysRemaining— Days RemainingnotBefore— Not BeforenotAfter— Not After
Pricing: $0.010 per domain (Pay-Per-Event) — about 100 domains per $1.
🤖 Use with AI agents
Point Claude, the OpenAI Agents SDK, an n8n flow or any MCP-aware client at it.
Sample agent prompt:
Agentic payments (x402): Supports agentic payment via x402 — call this actor with USDC, no API key required.
🔗 Related tools — Security audit toolkit
DMARC Auditor · Domain Security Posture · CVE Monitor · CISA KEV · Dependency Advisories · Chrome Extension Analyzer
A NexGenData utility actor.


